The cyber security specialists your business needs. Working as one team.
Your business depends on tight cyber security that keeps pace with a changing threat landscape, because if your business is not secure, neither are your clients, your growth or your revenue. Tell us what you need to protect or resolve. We assess where you stand, select independent specialists across six cyber security capabilities, and coordinate them under one plan, with one point of contact.
Not sure where you stand? Take the free 4-minute HealthCheck
 Cloud · DevSecOps
 Incident response · forensics
 SOC · MXDR · testing
 AI GRC · compliance
Experts in every capability. One coordinated plan.
Musketeers Security is the UK’s first cyber security consortium, bringing independent specialist firms together as one coordinated team. We assess what your business needs, select the member firms with the right expertise, and manage delivery under one plan with one point of contact.
Each firm works independently within its own field; Musketeers owns the coordination. You get targeted expertise from industry specialists, covering only what you actually need, without having to source or manage them yourself. As your business and the threats around it change, the team changes with them. And because cyber risk does not discriminate by company size, neither do we. Musketeers works with businesses of every size: all for security, security for all.
A single view of risk
Findings from each specialist are reviewed together and prioritised by their effect on your business.
A single delivery plan
You can see who owns each task, when it is due and what it depends on across all firms involved.
A single point of contact
One call at 2am starts the coordination of the response, including insurance, forensics and legal advisers.
Fragmented security leaves gaps.
Most cyber security providers are expert in one or two disciplines. None cover them all, yet a healthy business now depends on all of them being covered. So businesses contract with several suppliers, each on its own terms and each reporting on its own piece of the picture. What nobody provides is the layer in the middle: a single point of communication, coordination and management that keeps scope, dependencies and impact under control. Without it, every gap between suppliers becomes the client’s problem, and as attacks rise and regulators sharpen their penalties, those gaps are getting more expensive to leave open.
- 48%
Your clients carry your risk
of breaches now involve a third party.
If your systems or data are compromised, so are the clients who trust you with theirs. Their breach starts with yours.
Verizon DBIR 2026 - £3.29m
Your revenue takes the hit
average cost of a data breach to a UK organisation.
Downtime, recovery, ransom, fines and the customers who leave afterwards. The bill arrives long after the incident.
IBM Cost of a Data Breach 2025 (UK) - Required
Your growth gets gated
Cyber Essentials is a condition of UK government contracts handling personal data; large private buyers increasingly ask the same.
Bigger clients, tenders and insurers ask for evidence of security before they sign. Without it, you are filtered out before the conversation starts.
Cabinet Office PPN 09/23
- 15%
Nobody owns the whole risk
of UK businesses review the cyber risks posed by their immediate suppliers.
Each supplier is accountable for its own scope. When a risk crosses scopes, no one owns the gap, and the joining-up lands on you.
DSIT Cyber Security Breaches Survey 2025/26 - 41%
You pay for margin, not expertise
say fragmentation has pushed up their security procurement costs.
Every layer between you and the specialist adds cost and removes accountability.
IBM IBV & Palo Alto Networks 2025 - 88%
A bench is not a team of experts
of security professionals have seen a skills shortage cause a significant security consequence.
You get the people a consultancy has available, not the specialists the problem actually needs.
ISC2 Workforce Study 2025
The AAA Secure Method. Assess · Assemble · Act.
Good security starts with an honest picture of where you stand and what your business actually needs. Each supplier has its own responsibilities, contract and report. Musketeers looks across that work so that risks, dependencies and decisions are addressed together. We first establish what needs attention, then bring in the specialists to address it. Musketeers coordinates delivery and checks the evidence against the agreed completion criteria.
- 01
Assess
Review the current position across six capabilities. You receive the findings before deciding what to commission.
- 02
Assemble
Select the member firms with the expertise required for each agreed priority, and nothing you don’t need.
- 03
Act
Coordinate delivery through one shared plan. Ways to engage: Watch · Secure · Maintain.
Assess the need. Six specialist capabilities.
Open each capability to see what it covers and when you might need it. An assessment establishes which specialists your business needs now, and keeps that picture current as the landscape changes.
01 / 06 Incident Response & Cyber InsurancePrepare for the first 48 hours
Specialist response when an incident occurs, including out of hours, with support for evidence collection and insurance claims.
Read about Incident Response in detail02 / 06 Cyber & AI GRCShow how your controls work
Clear senior responsibility for cyber risk, regulatory requirements and AI use, supported by records that show whether controls work.
Read about Cyber & AI GRC in detail03 / 06 Attack SimulationTest how an attacker could get in
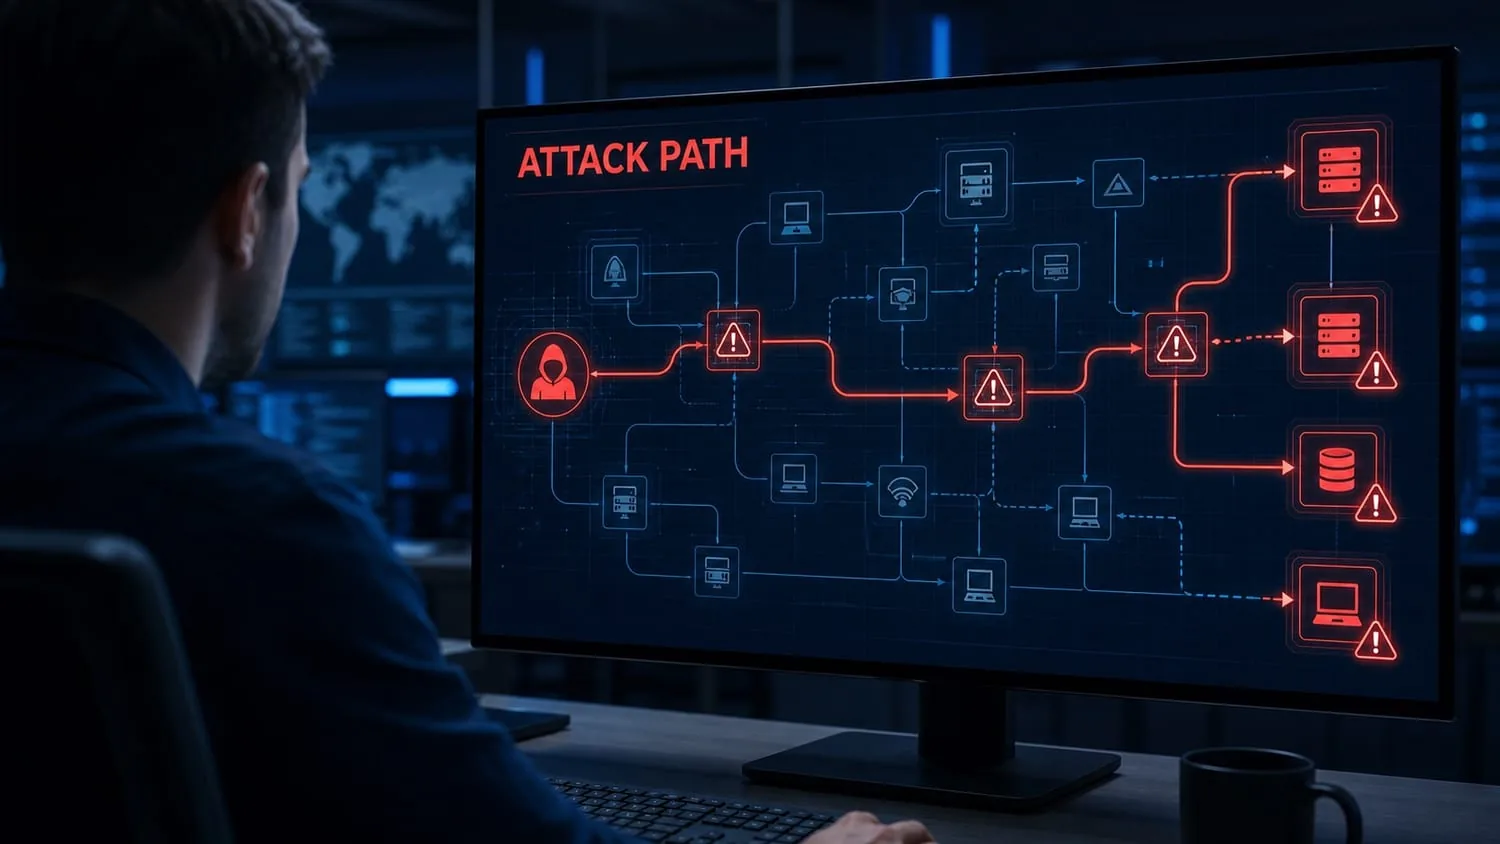
Authorised testing follows potential attack paths through your systems. It checks how weaknesses could be combined and whether your monitoring and response teams would detect the activity.
Read about Attack Simulation in detail04 / 06 Managed SecurityInvestigate and respond around the clock
Specialists monitor, investigate and respond to threats 24/7. Independent review checks what the service detects, how alerts are assessed and whether escalation works as intended.
Read about Managed Security in detail05 / 06 Cloud, Identity, AI & DevSecOpsControl access and secure change
Specialist work to secure cloud platforms, user and system access, AI use and software delivery.
Read about Cloud, Identity & AI in detail06 / 06 Third-Party Risk & Due DiligenceUnderstand the risk from your suppliers
Checks on suppliers, partners and acquisitions that can access your data or disrupt critical services.
Read about Third-Party Risk in detailAssemble the team. The member firms.
Each member contributes its own expertise. The assessment establishes which firms and skills your business needs, and nothing it does not.
Act on one plan. Let’s discuss what you need.
Tell us what you need to resolve, or where you suspect your security is falling short. We will help you decide where to start and which specialists to involve, so your security keeps pace with your business.